Zero Day Vulnerabilities - When Hackers Strike First
Technically U9 Aug 2025

Zero Day Vulnerabilities - When Hackers Strike First

🎯 Right now, there's a bullet with your company's name on it—and you can't see it coming.

Imagine waking up tomorrow to find your entire network compromised. Customer data stolen. Systems locked. Operations paralyzed. The worst part? Your million-dollar security stack didn't even blink.

This isn't fiction. This is the reality of zero-day attacks.

In 2023 alone, zero-day exploits caused $6.9 billion in damages globally. The victims? Household names like Microsoft, Google, Apple—and thousands of businesses that thought they were protected.

The terrifying truth: Your next breach might be happening right now, and you'll only find out when it's too late.


🚨 What You'll Discover:

The Invisible Threat Landscape:

  • Why zero-days are called "the nuclear weapons of cyberspace"
  • How the global zero-day market operates (hint: it's worth $12+ billion)
  • Which software you use daily has the most zero-day vulnerabilities

Legendary Attacks Decoded:

  • Stuxnet (2010): How the U.S. and Israel destroyed Iranian nuclear centrifuges with code
  • EternalBlue (2017): The NSA exploit that powered WannaCry and crippled hospitals worldwide
  • Pegasus Spyware: How zero-clicks hijacked world leaders' phones through iMessage
  • Operation Aurora (2009): China's zero-day assault on Google's source code
  • SolarWinds (2020): The supply chain zero-day that infiltrated 18,000 organizations

The Economics of Digital Warfare:

  • Government arsenals: Why the CIA stockpiles zero-days like missiles
  • Bug bounty programs: How companies pay millions to find flaws first
  • Dark web marketplaces: Where cybercriminals buy and sell digital weapons
  • Nation-state budgets: The $15 billion global spend on offensive cyber capabilities

Detection & Defense Strategies:

  • Behavioral analysis: How AI spots attacks that signatures miss
  • Zero Trust architecture: Building defenses that assume breach
  • Threat hunting: Proactive techniques that find hidden attackers
  • Deception technology: Honeypots and traps that catch zero-day users
  • Memory protection: The hardware-level defenses stopping exploitation

Industry Intelligence:

  • Which zero-days Microsoft, Apple, and Google fear most
  • How security researchers ethically discover and disclose flaws
  • The CVE system: Global coordination against unknown threats
  • Emergency patching protocols when zero-days go public

Future Warfare:

  • AI-discovered vulnerabilities: Machine learning finding flaws faster than humans
  • Quantum computing threats: How future technology will break current defenses
  • IoT zero-days: The coming storm of vulnerable connected devices

💰 The Billion-Dollar Blindside:

  • Equifax (2017): $700M+ settlement from a single vulnerability
  • WannaCry ransomware: $4 billion in global damages from one NSA exploit
  • NotPetya attack: $10 billion in worldwide economic impact

🎯 Who's Most at Risk:

  • Healthcare systems: 60% increase in zero-day targeting
  • Financial institutions: $18.3M average breach cost
  • Critical infrastructure: Power grids, water systems, transportation
  • Small businesses: 76% have no zero-day protection strategy

⚠️ Current Threat Level:

  • 43% increase in zero-day exploits discovered in 2023
  • Average 287 days between vulnerability creation and discovery
  • 68% of organizations can't detect zero-day attacks in their environment

🔥 Why This Episode Matters NOW:

  • Recent zero-days in popular software you probably use
  • New AI tools making vulnerability discovery faster for both sides
  • Upcoming regulations requiring zero-day preparedness

Real-World Impact StoriesUrgency Amplifiers

Don't be tomorrow's headline. Every day you wait to understand zero-day threats is another day attackers have the advantage. Subscribe now and arm yourself with the knowledge that could save your career—and your company.

#ZeroDay #Cybersecurity #CyberWarfare #InfoSec #ThreatIntelligence #Stuxnet #Pegasus #EternalBlue #CyberAttack #SecurityResearch #VulnerabilityManagement #ThreatHunting #ZeroTrust

Det här avsnittet är hämtat från ett öppet RSS-flöde och publiceras inte av Podme. Det kan innehålla reklam.

Avsnitt(270)

Pass-ta-Key Attacks: Is Passwordless Security Still Safe?

Pass-ta-Key Attacks: Is Passwordless Security Still Safe?

Apple, Google, Microsoft, and the security industry have spent years telling us that passkeys are the future of authentication.No passwords.Less phishing.No reusable credentials for attackers to steal...

12 Sep 23min
SaaS Bloodbath: Why Your Trusted Apps Are Now the Attack Surface

SaaS Bloodbath: Why Your Trusted Apps Are Now the Attack Surface

Your company may not get hacked through the firewall. It may get breached through the SaaS app everyone trusts.In this episode of Technically U, we break down the growing SaaS security crisis and why ...

5 Sep 36min
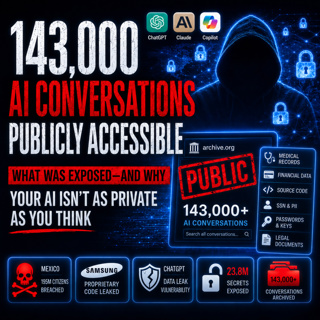
The AI Data Disaster: What ChatGPT, Claude, and Gemini Really Do With Your Secrets

The AI Data Disaster: What ChatGPT, Claude, and Gemini Really Do With Your Secrets

143,000 ChatGPT, Claude, and Copilot conversations are publicly accessible right now. Here's what was exposed—and why your AI isn't as private as you think.🚨 THE HEADLINE:143,000 user conversations w...

29 Aug 21min
The BIMI Paradox: Why 90% of Companies Are Losing Thousands.

The BIMI Paradox: Why 90% of Companies Are Losing Thousands.

The BIMI Paradox: Why 90% of Companies Are Losing Thousands—And Why Your Logo Might Be Illegal in Inboxes (2026 Reality Check).BIMI (Brand Indicators for Message Identification): 90% of companies have...

29 Aug 26min
Beyond Surveillance: How Behavioral Analytics Became a Trust Problem

Beyond Surveillance: How Behavioral Analytics Became a Trust Problem

Behavioral Analytics in 2026: How Companies Are Moving From Surveillance to Trust ArchitectureThe paradox nobody talks about: 76% of companies see efficiency gains from monitoring. But 60% of employee...

20 Aug 17min
The Confidence Gap: Why Executives Think AI Agents Are Secure (And Why They're Wrong)

The Confidence Gap: Why Executives Think AI Agents Are Secure (And Why They're Wrong)

The Confidence Gap: AI Agents and the Security Crisis Nobody Is Talking AboutEighty-two percent of executives feel confident that their existing AI agent policies are enough to keep their organization...

8 Aug 18min
Seeing Is No Longer Believing: How Deepfake Fraud Targets Businesses and Families

Seeing Is No Longer Believing: How Deepfake Fraud Targets Businesses and Families

What if the voice on the phone sounds exactly like your boss, your bank, or someone in your family — but it isn’t them?In this episode of Technically U, we break down Deepfake Fraud and why it has bec...

31 Juli 23min
The AI Criminal Playbook: How Cybercrime Changed Forever in 2026

The AI Criminal Playbook: How Cybercrime Changed Forever in 2026

The next generation of cybercrime may not come from a hacker typing code in a dark room.It may come from someone using AI to generate phishing emails, clone voices, create fake identities, manipulate ...

24 Juli 16min
Populärt inom Teknik

uppgang-och-fall
bilar-med-sladd
vi-bilagares-podcast
rss-ai-med-jonas-benjamin
market-makers
elbilsveckan
rss-laddstationen-med-elbilen-i-sverige
rss-technokratin
natets-morka-sida
rss-elektrikerpodden
rss-uppgang-och-fall
skogsforum-podcast
rss-snacka-om-ai
rss-en-ai-till-kaffet
bli-saker-podden
rss-veckans-ai
hej-bruksbil
developers-mer-an-bara-kod
rss-elektrifieringspodden
rss-sakerhetspodcasten