The BIMI Paradox: Why 90% of Companies Are Losing Thousands.

The BIMI Paradox: Why 90% of Companies Are Losing Thousands.

The BIMI Paradox: Why 90% of Companies Are Losing Thousands—And Why Your Logo Might Be Illegal in Inboxes (2026 Reality Check).

BIMI (Brand Indicators for Message Identification): 90% of companies have it wrong—and 75% will have it by year-end 2026.

Here's the reality behind the hype.

🎯 THE BIMI PARADOX (2026 REALITY):

ADOPTION STATISTICS:- 90.85% of domains have NO BIMI record- 4.57% have VALID BIMI records- 4.58% have INVALID BIMI records- BIMI adoption increased 340% year-over-year- Yet most implementations are failing silently

THE CONTRADICTION:

Adoption is exploding, but 95% are doing it wrong or not at all.---

💥 THE HYPE VS. REALITY:

WHAT YOU'VE HEARD:

❌ "BIMI increases open rates by 21%"

❌ "Get BIMI for engagement lifts"

❌ "BIMI is quick to implement"

THE REALITY (2026):

✅ BIMI increases trust and brand recognition (not opens)

✅ The 21% stat was from 2023 when BIMI was rare

✅ As adoption grows, novelty effect wears off (4-6% realistic lift now)

✅ Real value: Phishing prevention + professional credibility

✅ Open rate ROI: Modest at best, nonexistent at worst

✅ Implementation: 14-25 weeks minimum

THE LESSON:

Stop building business case around open rate increases. That's a failure case. The real ROI is in security and trust—which email spoofing and phishing attacks make incredibly valuable.---

🔒 WHAT BIMI ACTUALLY DOES:

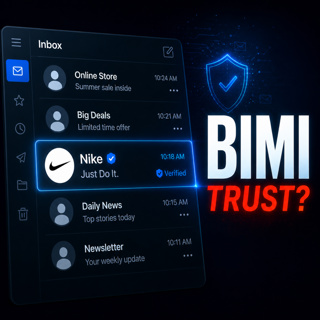
SIMPLE VERSION: Your verified brand logo appears next to your email in recipient inboxes (Gmail, Yahoo, Apple Mail, etc.)

SECURE VERSION: When an email arrives, the email provider:

1. Checks DMARC authentication (verified)

2. Looks up BIMI DNS record

3. Validates your certificate (VMC or CMC)

4. Fetches and displays your logo

5. Shows a checkmark indicating verification

RESULT:

Recipients see: [Blue Checkmark] [Your Logo] Your Company Name

Psychological signal: "This email is verified and legitimate"ANTI-PHISHING

IMPACT:

Phishing emails can't fake this verification. Attackers would need your certificate, which requires proving they own your domain. So when recipients see your verified logo, it's impossible to fake.---

📋 THE 4 REQUIREMENTS (WHAT MOST MISS):

REQUIREMENT 1:

DMARC ENFORCEMENT

❌ DMARC monitoring (p=monitoring) does NOT qualify

✅ DMARC enforcement REQUIRED (p=quarantine or p=reject)

Problem: Many orgs have DMARC monitoring but fear enforcement. So they stay stuck.

Status: Mandatory for bulk senders anyway (Gmail/Yahoo requirement)Timeline: 6-12 weeks to transition from monitoring to enforcement

REQUIREMENT 2: SVG TINY PORTABLE/SECURE FORMAT

❌ Standard SVG from Adobe Illustrator (won't work)

❌ Raster images embedded (not allowed)

❌ Scripts (not allowed)

❌ CSS styling issues (various restrictions)

✅ SVG Tiny PS format (exact specification required)

✅ Square logo (200x200px minimum)

✅ Valid baseProfile

✅ No scripts, no embedded images

Problem: Most organizations don't know this spec exists. Designer delivers standard SVG. Organization publishes invalid record. Logo never displays.

Status: Most common failure point (validation tools required)Timeline: 1-3 weeks with proper validation

REQUIREMENT 3:

CERTIFICATE (VMC or CMC)

✅ VMC (Verified Mark Certificate): • Requires registered trademark • Cost: $900-$1,700/year • Timeline: 4-8 weeks • Support: Gmail, Yahoo, Apple Mail (+ blue checkmark in Gmail)

✅ CMC (Common Mark Certificate) - NEW 2025: • Does NOT require trademark • Requires proof logo used 12+ months (archive.org) • Cost: ~$650/year • Timeline: 1-2 weeks • Support: Gmail, Yahoo (expanding)

❌ Self-Asserted BIMI: • No certificate required • Works on ~30% of inboxes (Yahoo, Fastmail) • NOT supported by Gmail/Apple • Only viable for startups/testing

Google's 2025 CMC announcement: Game changer. Eliminated trademark requirement. BIMI adoption jumped 340%.REQUIREMENT 4: HTTPS HOSTING

✅ Logo must be hosted on HTTPS (not HTTP)

✅ Valid TLS certificate from recognized CA

✅ Support for TLS 1.2+

Denne episoden er hentet fra en åpen RSS-feed og er ikke publisert av Podme. Den kan derfor inneholde annonser.

Episoder(270)

Pass-ta-Key Attacks: Is Passwordless Security Still Safe?

Pass-ta-Key Attacks: Is Passwordless Security Still Safe?

Apple, Google, Microsoft, and the security industry have spent years telling us that passkeys are the future of authentication.No passwords.Less phishing.No reusable credentials for attackers to steal...

12 Sep 23min
SaaS Bloodbath: Why Your Trusted Apps Are Now the Attack Surface

SaaS Bloodbath: Why Your Trusted Apps Are Now the Attack Surface

Your company may not get hacked through the firewall. It may get breached through the SaaS app everyone trusts.In this episode of Technically U, we break down the growing SaaS security crisis and why ...

5 Sep 36min
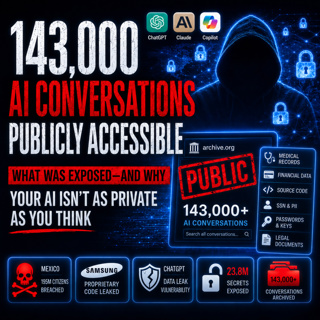
The AI Data Disaster: What ChatGPT, Claude, and Gemini Really Do With Your Secrets

The AI Data Disaster: What ChatGPT, Claude, and Gemini Really Do With Your Secrets

143,000 ChatGPT, Claude, and Copilot conversations are publicly accessible right now. Here's what was exposed—and why your AI isn't as private as you think.🚨 THE HEADLINE:143,000 user conversations w...

29 Aug 21min
Beyond Surveillance: How Behavioral Analytics Became a Trust Problem

Beyond Surveillance: How Behavioral Analytics Became a Trust Problem

Behavioral Analytics in 2026: How Companies Are Moving From Surveillance to Trust ArchitectureThe paradox nobody talks about: 76% of companies see efficiency gains from monitoring. But 60% of employee...

20 Aug 17min
The Confidence Gap: Why Executives Think AI Agents Are Secure (And Why They're Wrong)

The Confidence Gap: Why Executives Think AI Agents Are Secure (And Why They're Wrong)

The Confidence Gap: AI Agents and the Security Crisis Nobody Is Talking AboutEighty-two percent of executives feel confident that their existing AI agent policies are enough to keep their organization...

8 Aug 18min
Seeing Is No Longer Believing: How Deepfake Fraud Targets Businesses and Families

Seeing Is No Longer Believing: How Deepfake Fraud Targets Businesses and Families

What if the voice on the phone sounds exactly like your boss, your bank, or someone in your family — but it isn’t them?In this episode of Technically U, we break down Deepfake Fraud and why it has bec...

31 Jul 23min
The AI Criminal Playbook: How Cybercrime Changed Forever in 2026

The AI Criminal Playbook: How Cybercrime Changed Forever in 2026

The next generation of cybercrime may not come from a hacker typing code in a dark room.It may come from someone using AI to generate phishing emails, clone voices, create fake identities, manipulate ...

24 Jul 16min
Populært innen Teknologi

teknisk-sett
energi-og-klima
lydartikler-fra-aftenposten
nasjonal-sikkerhetsmyndighet-nsm
smart-forklart
tomprat-med-gunnar-tjomlid
elektropodden
rss-ai-forklart
shifter
pedagogisk-intelligens
fornybaren
kortslutning
rss-bouvet-bobler
rss-ki-praten
rss-teknologioptimistene-en-podkast-om-teknologi-og-mennesker
rss-alt-som-gar-pa-strom
rss-larervarelset
rss-digitaliseringspadden
hans-petter-og-co
rss-bits-and-bytes-for-advokater