Secuestro Digital en el BHU: Doble Extorsión, 700GB Robados y el “Protocolo del Silencio” que Ocultó la Amenaza a los Clientes.

Secuestro Digital en el BHU: Doble Extorsión, 700GB Robados y el “Protocolo del Silencio” que Ocultó la Amenaza a los Clientes.

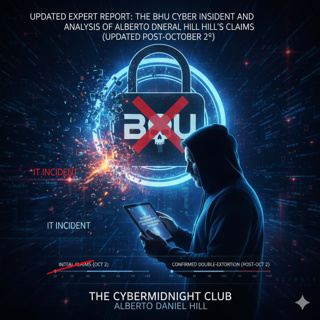
BHU (Banco Hipotecario del Uruguay)The bank's initial public response severely minimized the true gravity of the digital threat by characterizing it as a routine technical issue, while in reality, the institution was the victim of a large-scale data theft, cryptocurrency ransom demand, and digital extortion.The contradictions between the official statement and the actual severity of the attack include:Minimizing the Event's NatureThe official institutional narrative and some initial media reports described the event using highly technical and benign language, which contradicted the underlying criminal activity:Official Narrative: The initial public response from the BHU (Banco Hipotecario del Uruguay) and sources like Montevideo Portal referred to the crisis as an "incidente informático" (IT incident) or "problema técnico".Actual Severity: This was not a technical failure but a "toma digital" (digital takeover) and an act of digital extortion. It was explicitly identified as a ransomware attack, where the ransom was demanded in bitcoins. Crypto24, the antagonist group, had published their direct threat on the Dark Web.Omitting Theft and ExtortionThe official bank communications focused on protective measures while omitting the critical elements of theft and ransom:Official Narrative: The BHU's official communication stated that the network was "dio de baja la red por precaución" or shut down to "proteger la información".Actual Severity: The severity stemmed from the fact that the attackers, Crypto24, had already infiltrated the systems and stolen the data. The system began to fail, and the public website went down at . The bank's network shutdown was an effort to protect the information, but the sources question if this was protection "De los atacantes o del público".The bank's official communique omitted any mention of the extortion or the robbery of data.Concealing the Magnitude of Data CompromiseWhile the bank spoke of "precaución," the sheer volume and sensitivity of the compromised data revealed a catastrophic breach:Actual Severity: Crypto24 not only encrypted the data but also stole 700 gigabytes (GB).The stolen information included legal contracts, records contables (accounting records), and datos personales de clientes (personal data of clients).The bank was facing a double extortion scenario: if they did not pay, the data would be exposed. Crypto24 issued a time-sensitive threat: "You have 72 hours. After that, we release everything". Later, the threat was partially fulfilled when "Parte de los datos fueron publicados".In essence, the initial institutional silence and the use of the term "incidente informático" contrasted sharply with the reality of having 700 GB of client data stolen and being under a direct, publicly viewable cryptocurrency ransom threat on the Dark Web

https://open.spotify.com/show/3XmolWa59mJtPWQsVyrKb9?si=ca8381e1d900475f


https://cybermidnight.club/secuestro-digital-en-el-bhu-doble-extorsion-700gb-robados-y-el-protocolo-del-silencio-que-oculto-la-amenaza-a-los-clientes/

Denne episoden er hentet fra en åpen RSS-feed og er ikke publisert av Podme. Den kan derfor inneholde annonser.

Episoder(1035)

 UAlberta.ca Deep Dive: Institutional Technical Debt, Peer Apathy & The Cybermidnight Lens.

UAlberta.ca Deep Dive: Institutional Technical Debt, Peer Apathy & The Cybermidnight Lens.

Show Notes: In this 360-degree forensic deep dive, Alberto Daniel Hill unpacks the sprawling cybersecurity case study of uAlberta.ca—analyzing the 2023 BeeHive Systems vulnerability scan that uncovere...

7 Okt 1h 1min
Cas uAlberta.ca : Dette Technique Institutionnelle, Apathie des Pairs et l'Axe Cybermidnight.

Cas uAlberta.ca : Dette Technique Institutionnelle, Apathie des Pairs et l'Axe Cybermidnight.

Notes de l'Épisode : Dans cette analyse médico-légale à 360 degrés, Alberto Daniel Hill décortique le cas emblématique de la sécurité informatique de l'Université de l'Alberta (uAlberta.ca), en s'appu...

7 Okt 20min
Caso uAlberta.ca: Deuda Técnica Institucional, Apatía del Sector y el Enfoque Cybermidnight.

Caso uAlberta.ca: Deuda Técnica Institucional, Apatía del Sector y el Enfoque Cybermidnight.

Notas del Episodio: En este análisis forense integral de 360 grados, Alberto Daniel Hill desglosa el caso de ciberseguridad de la Universidad de Alberta (uAlberta.ca), examinando el informe de escaneo...

7 Okt 24min
Grabación Original: H1 - El Regreso Más Poderoso (Audio Raw Completo / X Space)

Grabación Original: H1 - El Regreso Más Poderoso (Audio Raw Completo / X Space)

🇪🇸 DESCRIPCIÓN EN ESPAÑOL (SPOTIFY)🎙️ Título del EpisodioGrabación Original: H1 - El Regreso Más Poderoso (Audio Raw Completo / X Space)Escucha la grabación íntegra y sin cortes del histórico X Spa...

29 Sep 3h 33min
Bandido Boss & The Fear Factory: Inside LATAM Cybercrime, Extortion SaaS, and Threat Manufacturing

Bandido Boss & The Fear Factory: Inside LATAM Cybercrime, Extortion SaaS, and Threat Manufacturing

🎙️ Spotify Episode TitleBandido Boss & The Fear Factory: Inside LATAM Cybercrime, Extortion SaaS, and Threat ManufacturingFrom multi-million dollar bank heists and cibernarco corridos to private thre...

29 Sep 52min
The Architecture of a Frame-Up

The Architecture of a Frame-Up

Show Title: The Architecture of Remorse — An Immersive Audio Drama by Alberto Daniel Hill[1][4]Episode Title: *EXTRA EPISODE — The Architecture of a Frame-Up (Progreso, Canelones · Tarantino Cut)*[2]S...

29 Sep 5min
MASTER DEEP DIVE — Alberto Daniel Hill's AI Architecture of Remorse: The Complete 5-Season Saga & Bonus Arcs

MASTER DEEP DIVE — Alberto Daniel Hill's AI Architecture of Remorse: The Complete 5-Season Saga & Bonus Arcs

EPISODE TITLE:MASTER DEEP DIVE — Alberto Daniel Hill's AI Architecture of Remorse: The Complete 5-Season Saga & Bonus ArcsWhat happens when a cybersecurity expert wrongfully jailed by the state turns ...

29 Sep 43min
EXTRA EPISODE — Progreso, Canelones: The Scapegoat Protocol

EXTRA EPISODE — Progreso, Canelones: The Scapegoat Protocol

FULL SHOW NOTES / DESCRIPTION:May 2026. A 19-year-old kid from Progreso, Canelones is arrested in a dawn raid. The headlines scream: "Leader of PampaLeaks Neutralized!" But behind the televised press ...

29 Sep 6min
Populært innen True crime

krimpodden-vg
avhort
podme-krim
rss-avhort-aktuelt
krimarkivet-2
rss-henlagt-andy-larsgaard
rss-svarttrost
rss-pa-innsiden-av-psychohoder
rss-espen-lee-usensurert
rss-domt-2
verdens-verste
forsvinningsfredag-podkast
kriminalkrniken
truecrimepodden-2
rss-domt-3
krimpodden-orderud
blalys
rss-siktet
truecrimepodden-dokumentar
rss-tause-vitner